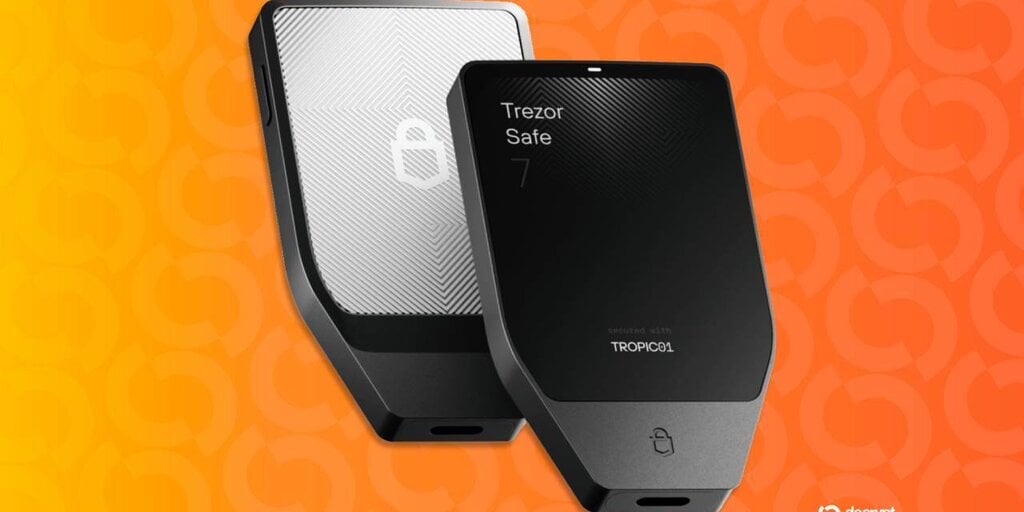
Hardware wallet manufacturer Trezor announced a reduction in its authorized reseller network as a preventive measure following reports of malicious hardware implants discovered in devices sold by competitor Ledger. In a statement on X, Trezor clarified that there is no evidence its own devices have been compromised, but cited recent supply-chain incidents as the reason for tightening distribution controls. Chief Commercial Officer Danny Sanders confirmed that certain resellers would be removed from the authorized list effective January 1, with shipments halted immediately.
The decision follows Ledger’s confirmation that at least one device purchased through Southeast Asian reseller CryptoBilis contained an unauthorized implant capable of capturing recovery phrases and transmitting them via cellular networks. This tampering method does not modify firmware, bypassing standard counterfeit detection checks. While CryptoBilis was also an authorized Trezor reseller, it suspended all hardware wallet sales during the investigation. European retailer MediaMarkt similarly removed Ledger products from its stores as a precautionary step.
Blockchain researchers estimate potential user losses between $72 million and $86 million, though Ledger has not yet confirmed the total number of affected users or the exact value lost. Trezor advised customers to purchase directly from the company, verify seal integrity, and consider multisignature setups using devices from different manufacturers to mitigate single-point failures.
Trezor’s move highlights the fragility of hardware security when physical supply chains are compromised by sophisticated, non-firmware-based attacks. By reducing resellers, the company prioritizes direct control over distribution channels, acknowledging that traditional software verification methods cannot detect hardware implants that read screen data externally. This shift underscores a growing industry recognition that trust must be anchored in provenance rather than just product integrity at the point of sale.
The incident exposes significant operational risks for consumers relying on third-party vendors, even those previously deemed authorized. As investigations into the Ledger breaches continue, the market may see increased demand for direct-to-consumer models and multisignature solutions that diversify risk across multiple hardware providers. Regulatory scrutiny of hardware wallet supply chains could intensify if loss estimates solidify, potentially forcing stricter certification standards for distributors.