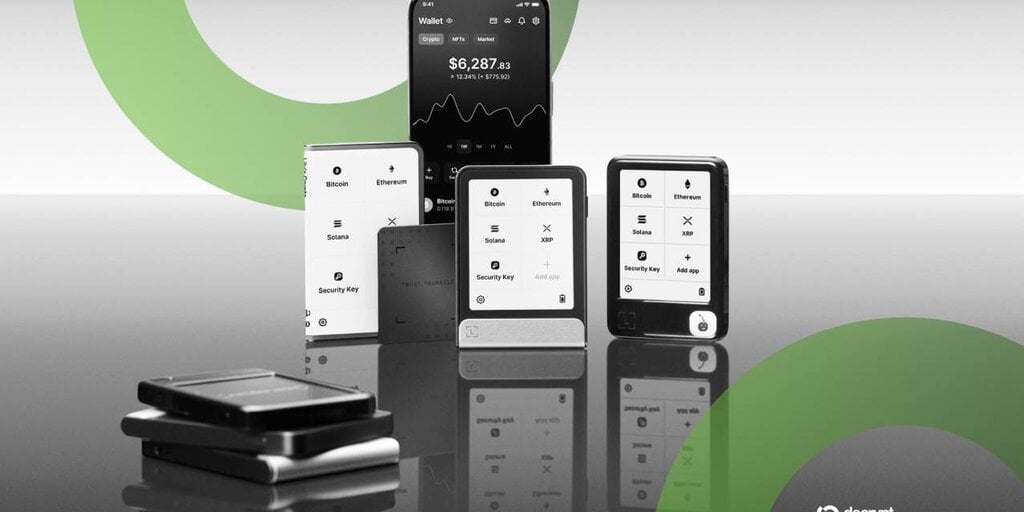
Ledger has initiated an investigation into fund losses reported by customers in Southeast Asia who purchased hardware wallets from a Malaysia-based reseller, CryptoBilis. The company confirmed on Saturday that one of the affected devices contained an unauthorized hardware implant designed to compromise security. While Ledger declined to specify the total amount lost, blockchain investigator Specter estimated that $86 million had been drained from these compromised units.
The incident came to light after users reported losing funds last week following purchases from CryptoBilis, a vendor based in Kuala Lumpur. In response, Ledger advised customers who bought from this specific reseller not to set up their devices and stated it was working with relevant authorities. The manufacturer emphasized that the number of impacted products appeared to be "limited" and noted that CryptoBilis has since ceased selling its hardware wallets.
Ledger issued a strong warning against purchasing from unauthorized resellers, citing the significant risk of acquiring suspicious, counterfeit, or modified devices that do not operate under Ledger’s security guidelines. The company acknowledged that security is not static and reaffirmed its commitment to continuously reviewing and strengthening distribution and anti-tamper processes. Neither Ledger nor CryptoBilis immediately responded to further inquiries regarding the specifics of the breach.
This incident highlights the critical vulnerability inherent in the supply chain for self-custody hardware, where physical tampering can bypass software-level security measures. Unlike remote exploits, the insertion of a hardware implant requires direct access to the device before it reaches the end user, suggesting that the compromise occurred at the distribution level rather than through a flaw in Ledger's core firmware or chip architecture. The reliance on authorized channels becomes paramount when the threat vector involves physical modification of the signing device itself.
From a Market Structure perspective, the event underscores the risks associated with gray-market resellers who may lack rigorous quality control or anti-tamper protocols. While Ledger reassured users that the scope was limited, the potential loss of $86 million indicates a severe impact on affected individuals. This situation may prompt stricter enforcement of distribution agreements and increased scrutiny of third-party vendors in emerging markets, as manufacturers seek to isolate their brand reputation from unauthorized intermediaries who cannot guarantee the integrity of the hardware they sell.